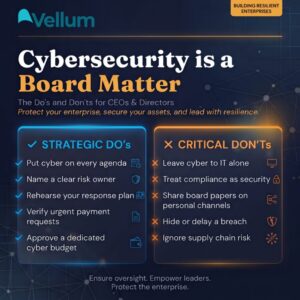
Cybersecurity Is a Board Matter: Do’s and Don’ts for Directors
October is Cybersecurity Awareness Month, and the Vellum team is marking it with a series of short, practical briefs for corporate leaders. This week, we turn to the boardroom to focus on the do’s and don’ts every director should know about cyber risk.
Cybersecurity is the practice of protecting systems, networks, programs, and data from digital attacks, unauthorized access, or damage. Cyber incidents are no longer simply an IT problem. A ransomware attack, data breach, or fraudulent transfer authorised by a spoofed email can halt operations, trigger regulatory action, and damage a reputation built over decades. Under the Data Protection Act, 2019; the Computer Misuse and Cybercrimes Act, 2018; and directors’ duties of care under the Companies Act, 2015, responsibility for overseeing cyber risk rests squarely with the board.